
Improve Cyber Security Response: 4 Benefits of Microsoft Sentinel Add-ons
4 ways Microsoft Sentinel benefits your cyber security response.
Threat Detection and Response: 3 compelling reasons why you should adopt automation
Modern threat detection automation does not replace analyst judgment-it enhances it. An automated workflow ingests raw telemetry, enriches the alert with asset context, and applies pre-set suppression logic for benign noise. When potential threats are identified, the system presents a fully contextualized incident to the SOC analyst for final approval and response execution. By maintaining […]
Cyber Security Visualization: Exploring the Possibilities
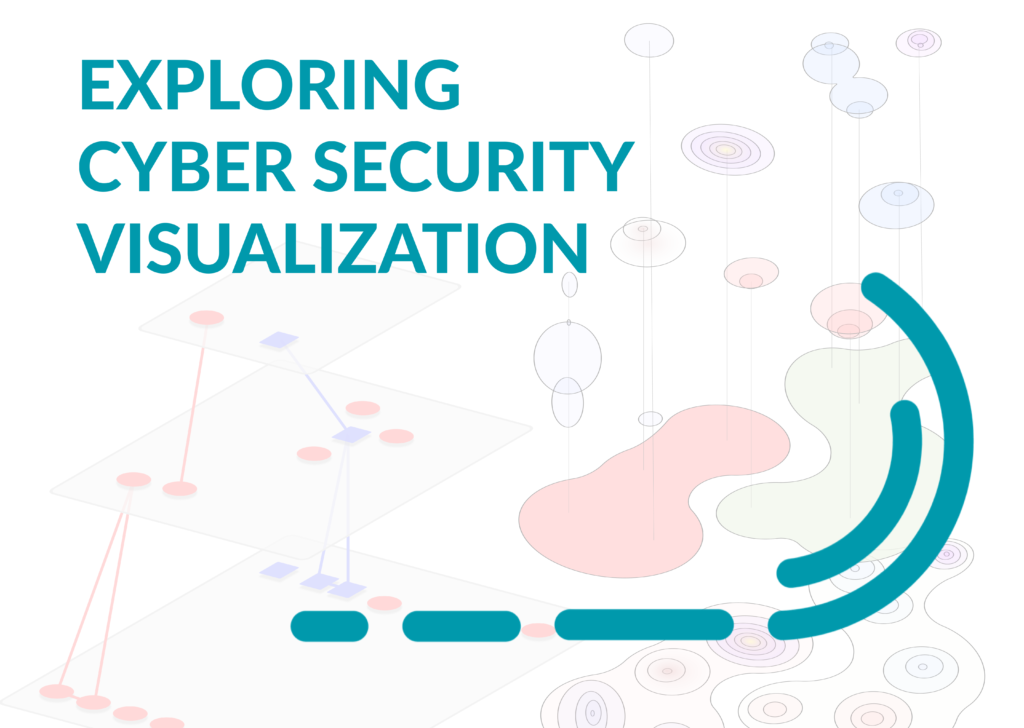
The cyber security visualization project between Seculyze, VENZO_ Cyber Security, and the IT University of Copenhagen aims to translate the one-dimensional list view of traditional analyst tools into interactive graph views for defenders. The vision is to design the next generation of analyst tools for the cyber security workforce. If you’re defending the king’s valley, […]
Microsoft Sentinel Tips: the 5 best ways to unlock the full power of Microsoft Sentinel
Microsoft Sentinel tips are 5 ways analysts can unlock more power from Microsoft Sentinel. With more value from Microsoft Sentinel, analysts can react faster and better against high-risk threats.
Incident Response: How to Manage Excessive Alerts
With an ever-increasing amount of cyberattacks, organizations are having to shift through more and more cyber alerts to defend themselves. Security teams are struggling to keep up. The incidence response suffers – with expensive consequences for the business.
Enriching your security alerts with added data can help you tune-out irrelevant alerts, and accelerate the analysis process. We explain how you can stay on top of an increasing amount of security alerts and optimize your incident response.