
Modern threat detection automation does not replace analyst judgment-it enhances it. An automated workflow ingests raw telemetry, enriches the alert with asset context, and applies pre-set suppression logic for benign noise. When potential threats are identified, the system presents a fully contextualized incident to the SOC analyst for final approval and response execution.
By maintaining human oversight in automated workflows, security teams achieve fast response times without sacrificing control or accuracy.
1. Reducing Repetitive Triage and Noise
One of the primary bottlenecks in incident response is the time spent on benign alerts. Security analysts often spend hours validating routine administrative actions that pose no threat.
Automated rule calibration and triage allow known benign patterns to be categorized or suppressed automatically. By leveraging Seculyze Tune, teams can automate alert calibration in Microsoft Sentinel, eliminating repetitive false positives and freeing up valuable analyst hours for high-fidelity threat hunting.
To see how autonomous workflows are taking triage a step further, read our guide on how Agentic AI solves specific SOC problems in Microsoft Sentinel
2. Enriched Context for Faster Decision-Making
When a threat actor targets an organization, seconds count. However, investigating an alert manually requires switching between multiple portals to check identity risk, asset criticality, and historical log activity.
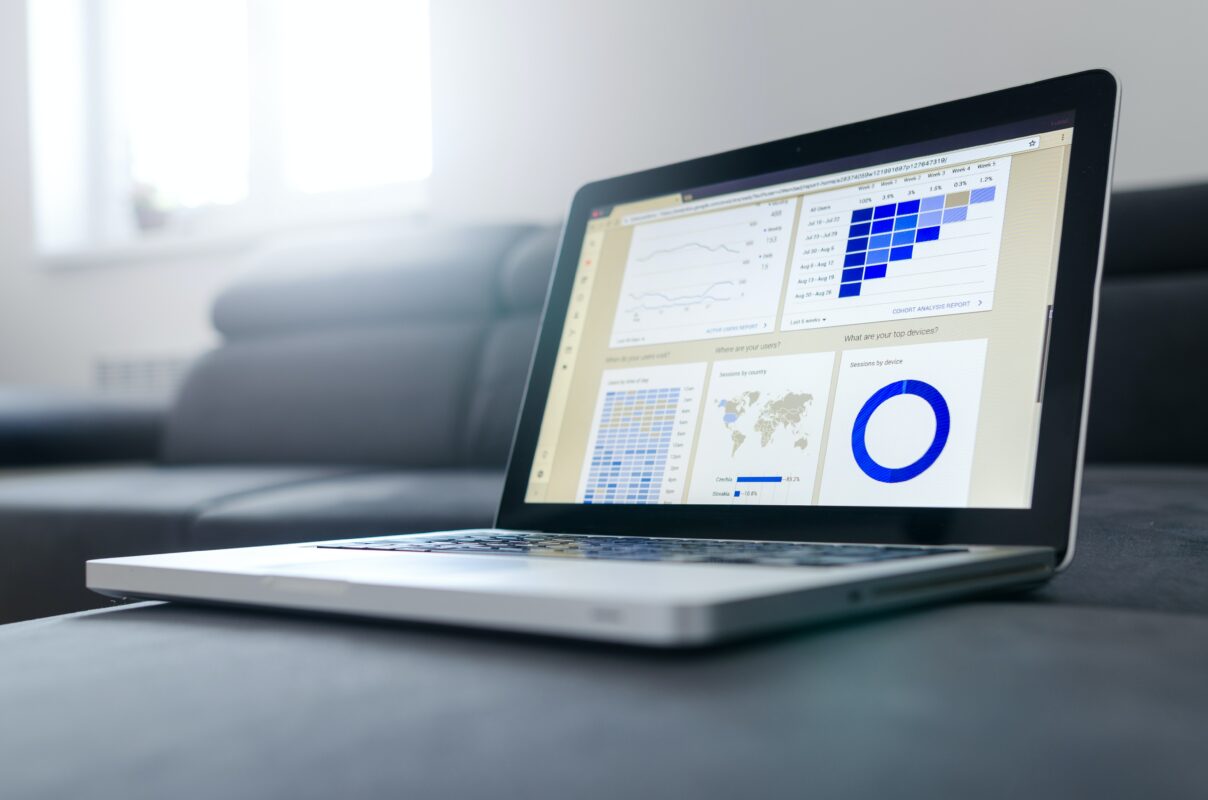
Automated threat detection solutions pull this contextual data automatically the moment an alert triggers. Delivering fully enriched telemetry directly into the incident view significantly reduces mean time to detect (MTTD) and mean time to respond (MTTR).
3. Continuous Detection Optimization
Threat landscapes change constantly, and detection logic must adapt alongside them. Static analytics rules can quickly become misconfigured or obsolete, creating hidden coverage gaps.
Automation significantly reduces MTTD and streamlines triage by cutting repetitive manual tasks while ensuring detection health is monitored continuously. Using Seculyze Calibrate, security leads can maintain continuous visibility over their detection rules and align coverage with established security frameworks like MITRE ATT&CK.
Streamline Your SOC Automation
Implementing intelligent automation allows your security team to focus on investigating real attacks rather than managing alert queues.
👉 Discover how Seculyze Tune optimizes threat detection in Microsoft Sentinel
Conclusion
The benefits of automating repetitive tasks in threat detection and response cannot be overstated. Automation saves valuable time, reduces human error in decision-making, and optimizes operational costs. By leveraging automated tools, your team can accurately prioritize high-fidelity alerts and ensure fast, effective incident response.
Need help automating your threat detection workflows? Seculyze offers a simple, powerful solution for Microsoft Sentinel.
Seculyze functions as an integrated add-on to Microsoft Sentinel, providing automated alert enrichment, rule tuning, and health checks-helping you respond faster to threats with greater accuracy. Find out more about Seculyze Tune here.
 Baselining user behavior by machine learning
Add security intelligence to our software that can predict which alerts are based on "normal" behavior and should be prioritized down. Read article
 What is MDR and what are its benefits?
As a professional threat detection and response service, MDR teams are comprised of cybersecurity experts who help organizations detect, respond, mitigate, and recover from... Read article